Windows Recon: SMB Nmap Scripts
Classification: Assessment Methodologies / Footprinting & Scanning
Target: demo.ine.local (10.2.31.54 - Windows Server 2008 R2 / 2012, host WIN-OMCNBKR66MN)
Credentials provided: administrator:smbserver_771
1. Executive Summary
The goal is to fingerprint and enumerate the SMB service of a Windows target using Nmap
NSE scripts. We confirm the host is up, discover the open SMB port, and then run a series
of smb-* scripts to enumerate protocol dialects, the security configuration, active
sessions, shares, domains, groups, services and share contents. The scans reveal dangerous
defaults (SMBv1 enabled, message signing disabled) and, with the provided administrator
credentials, full READ/WRITE access to C$.
2. Host Discovery & Port Scan
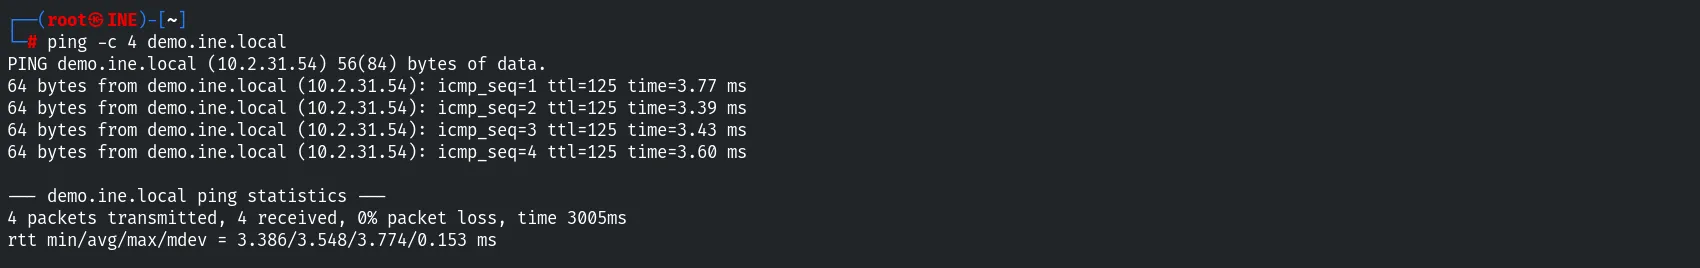
ping -c 4 demo.ine.localThe TTL of 125 is consistent with a Windows host.
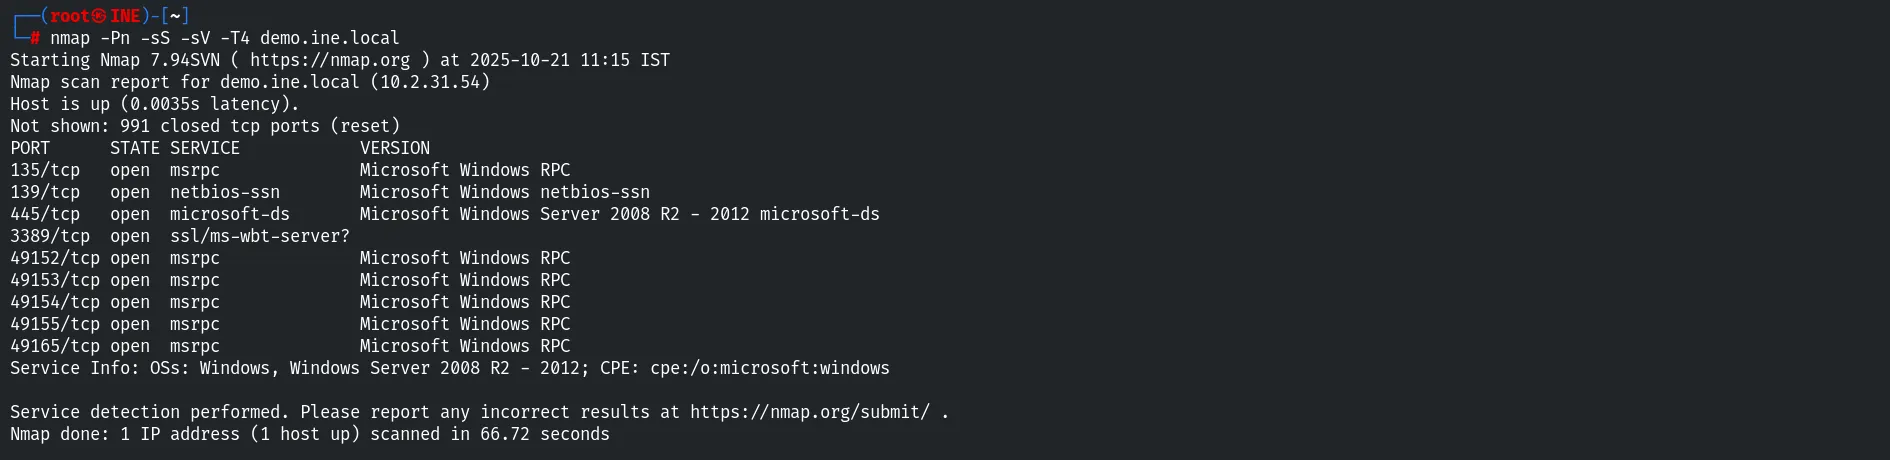
nmap -Pn -sS -sV -T4 demo.ine.localPorts 135, 139, 445, 3389 and several high MSRPC ports are open; the OS is identified as Windows Server 2008 R2 - 2012.
3. SMB Protocol Dialects
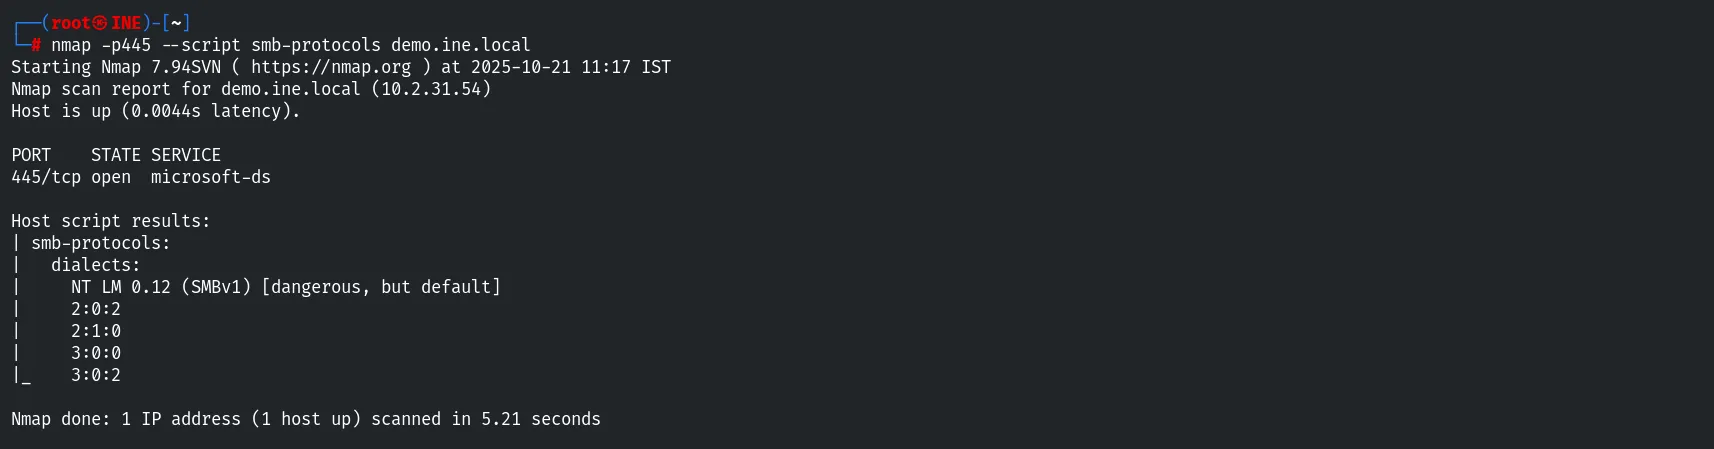
nmap -p445 --script smb-protocols demo.ine.localThe server supports NT LM 0.12 (SMBv1) [dangerous, but default] as well as SMB 2.0.2, 2.1, 3.0 and 3.0.2.
4. SMB Security Mode
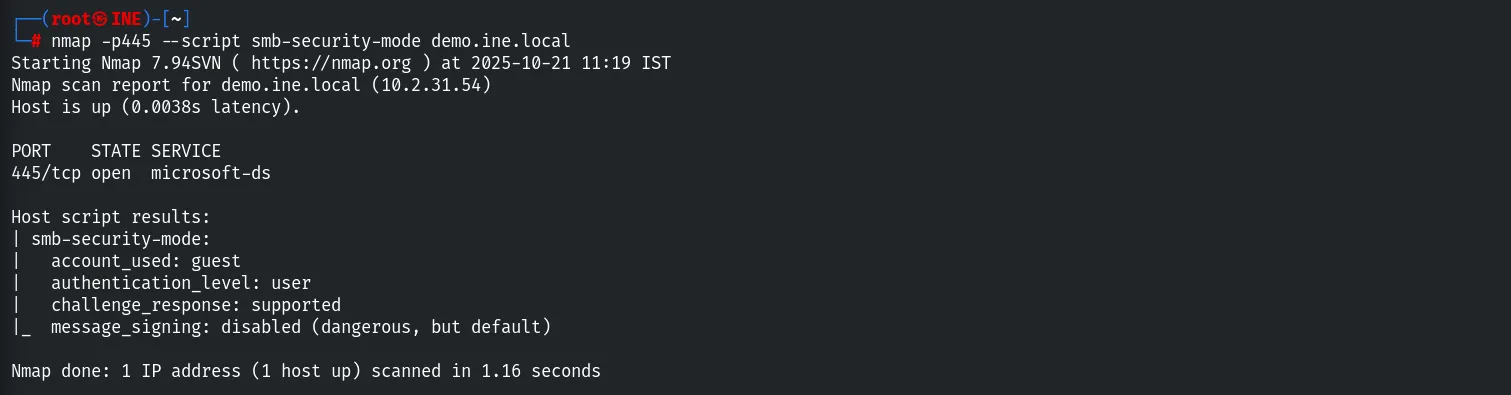
nmap -p445 --script smb-security-mode demo.ine.localMessage signing is disabled (dangerous, but default), which exposes the host to SMB relay attacks.
5. Session Enumeration
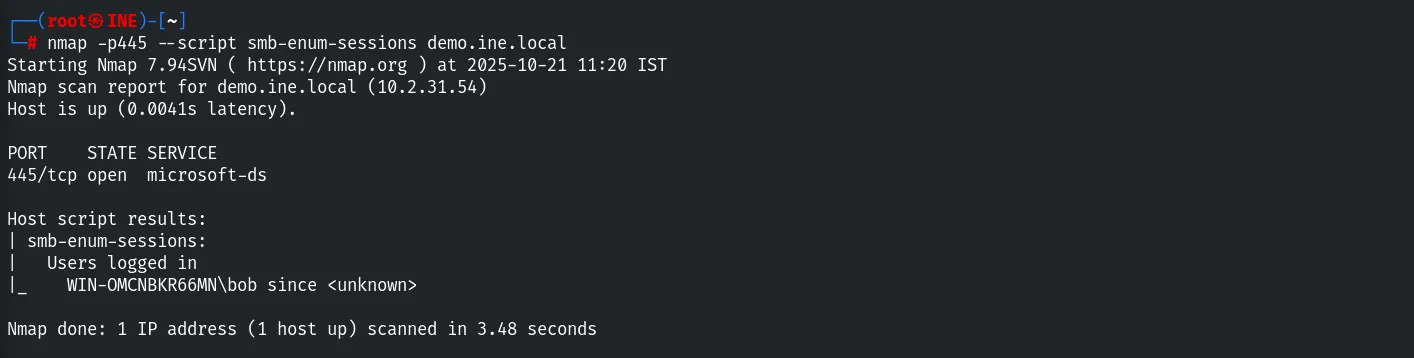
nmap -p445 --script smb-enum-sessions demo.ine.localWithout credentials we can already see that WIN-OMCNBKR66MN\bob is logged in.
Supplying the provided credentials reveals additional detail, including the active
ADMINISTRATOR session connected from 10.10.49.2.
nmap -p445 --script smb-enum-sessions --script-args smbusername=administrator,smbpassword=smbserver_771 demo.ine.local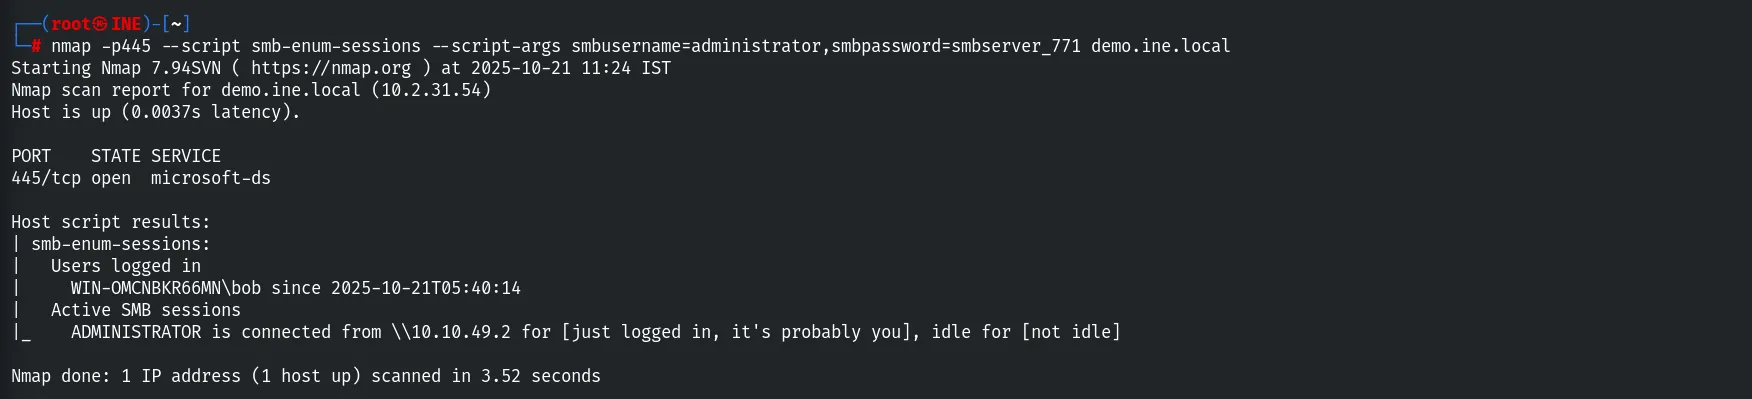
6. Share Enumeration (guest)
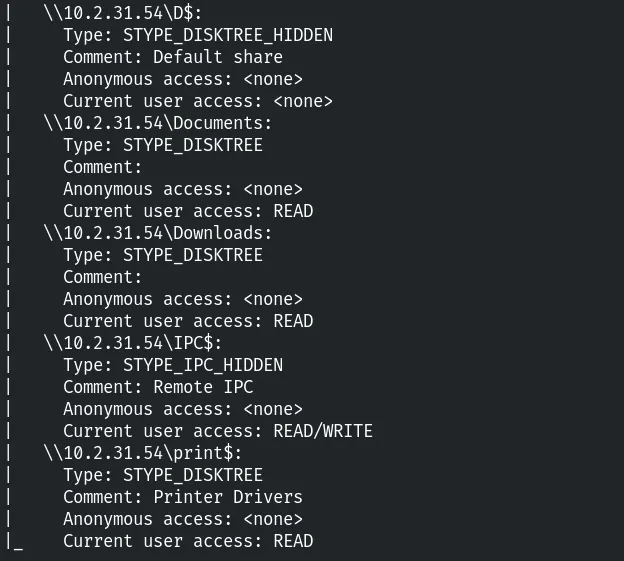
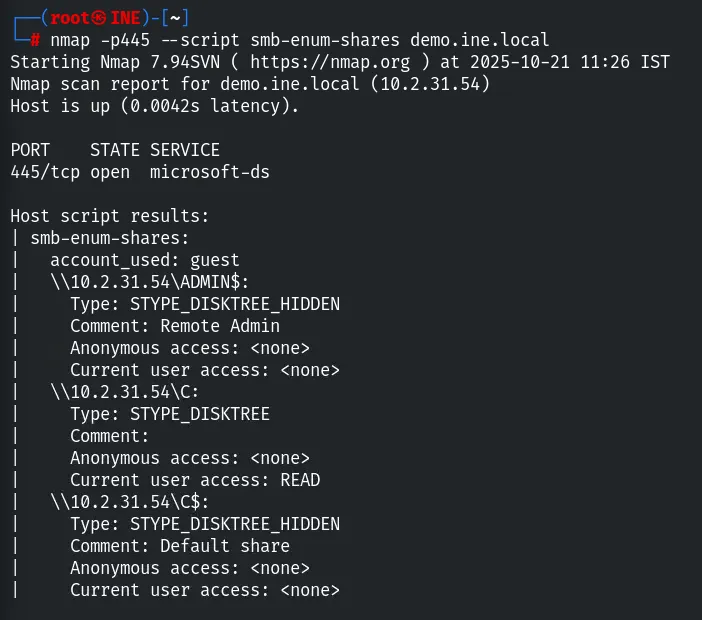
nmap -p445 --script smb-enum-shares demo.ine.localAs the guest account, we enumerate the shares and their access levels. IPC$ and the
per-user Documents/Downloads shares are readable.
7. Share Enumeration (authenticated)
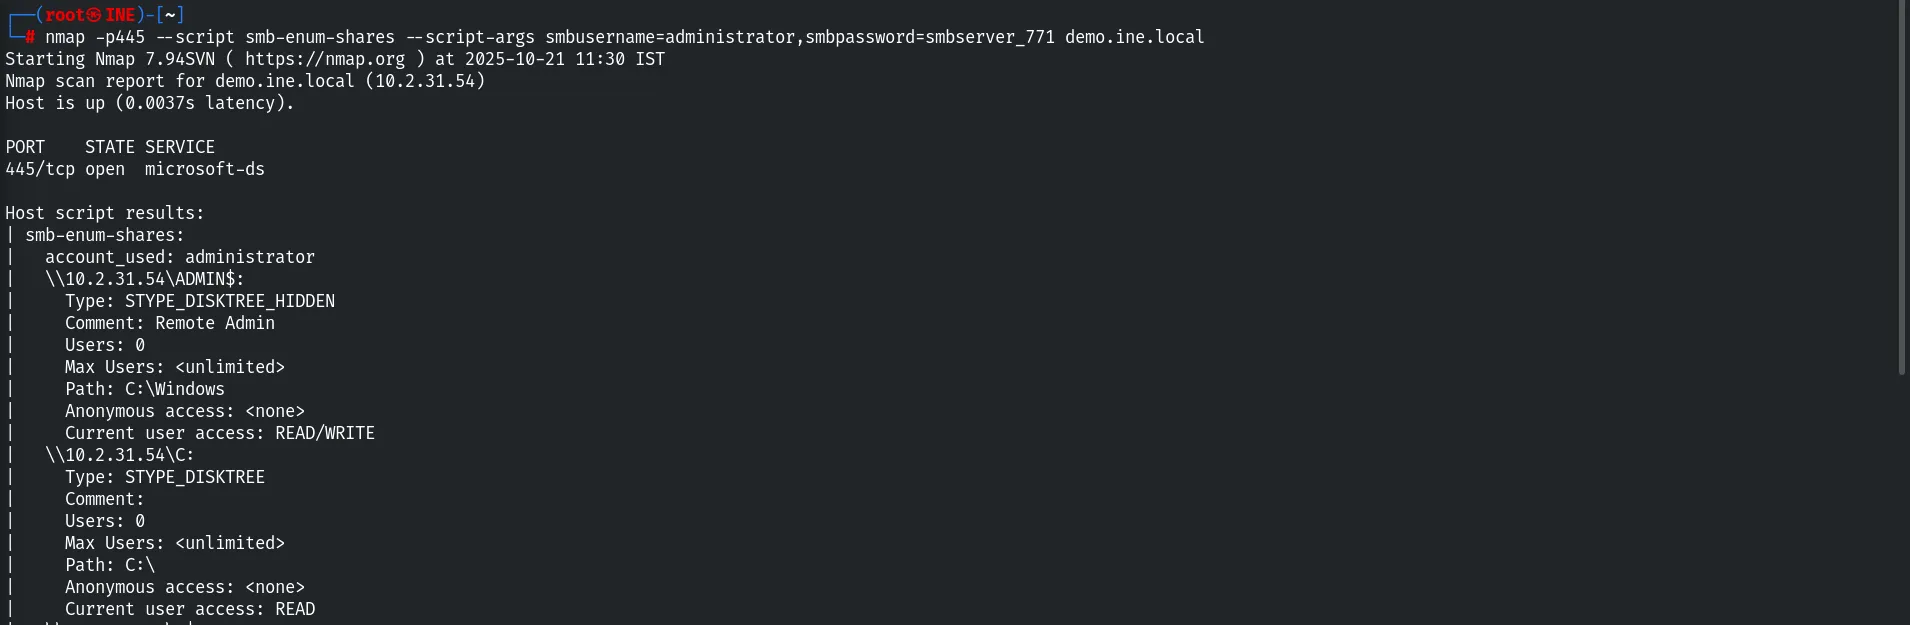
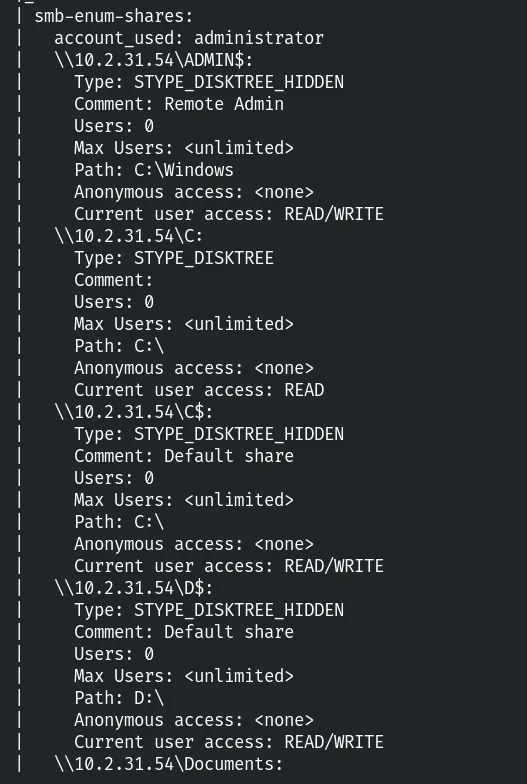
nmap -p445 --script smb-enum-shares --script-args smbusername=administrator,smbpassword=smbserver_771 demo.ine.localAuthenticated as administrator, we now have READ/WRITE access to ADMIN$ (C:\Windows)
and the entire C$.
8. Server, Domain, Group & Service Enumeration
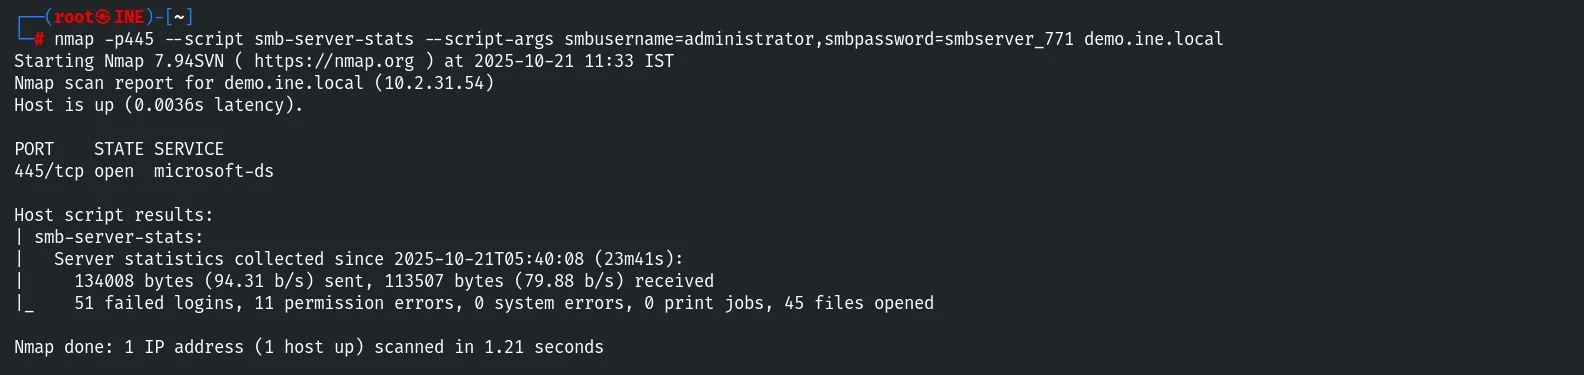
nmap -p445 --script smb-server-stats --script-args smbusername=administrator,smbpassword=smbserver_771 demo.ine.localServer statistics show 51 failed logins and 11 permission errors.
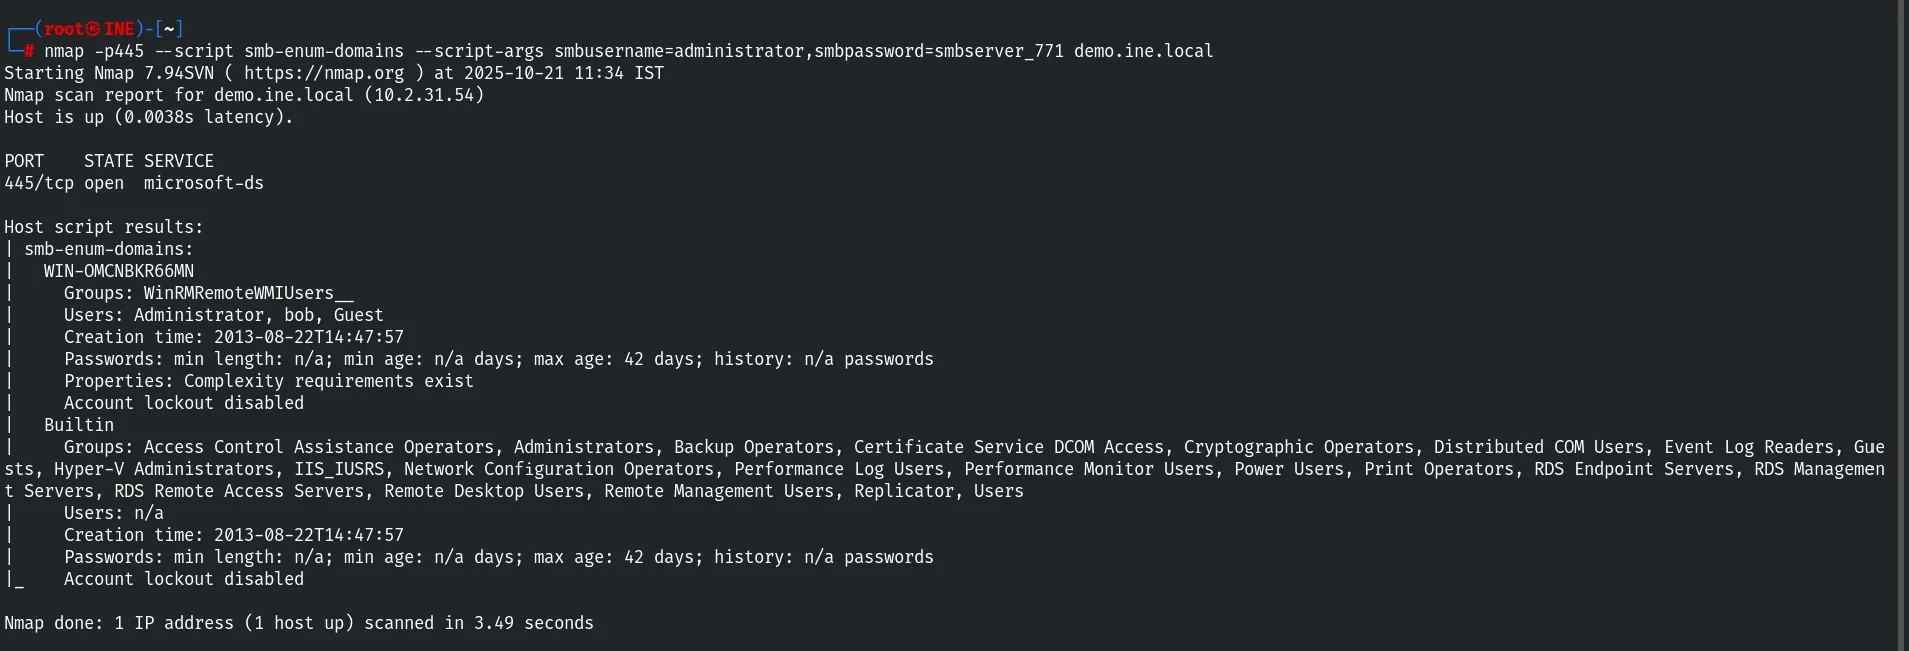
nmap -p445 --script smb-enum-domains --script-args smbusername=administrator,smbpassword=smbserver_771 demo.ine.localDomain information lists the users Administrator, bob, Guest, password policy
(complexity required, account lockout disabled) and the built-in groups.
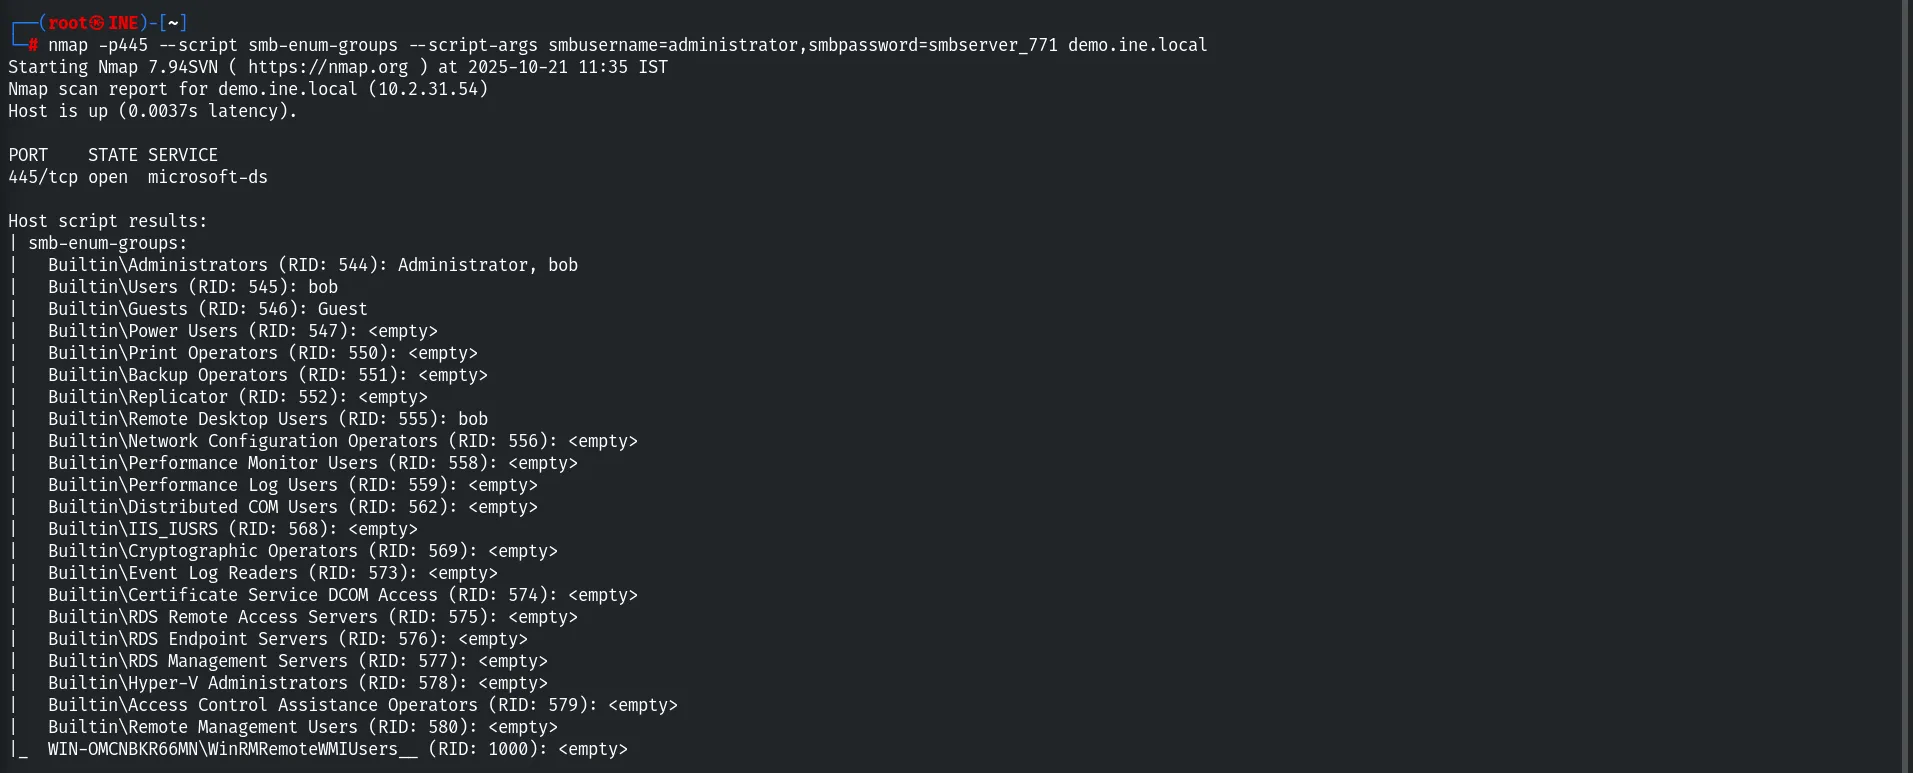
nmap -p445 --script smb-enum-groups --script-args smbusername=administrator,smbpassword=smbserver_771 demo.ine.localGroup membership shows Administrators: Administrator, bob and Remote Desktop Users: bob.
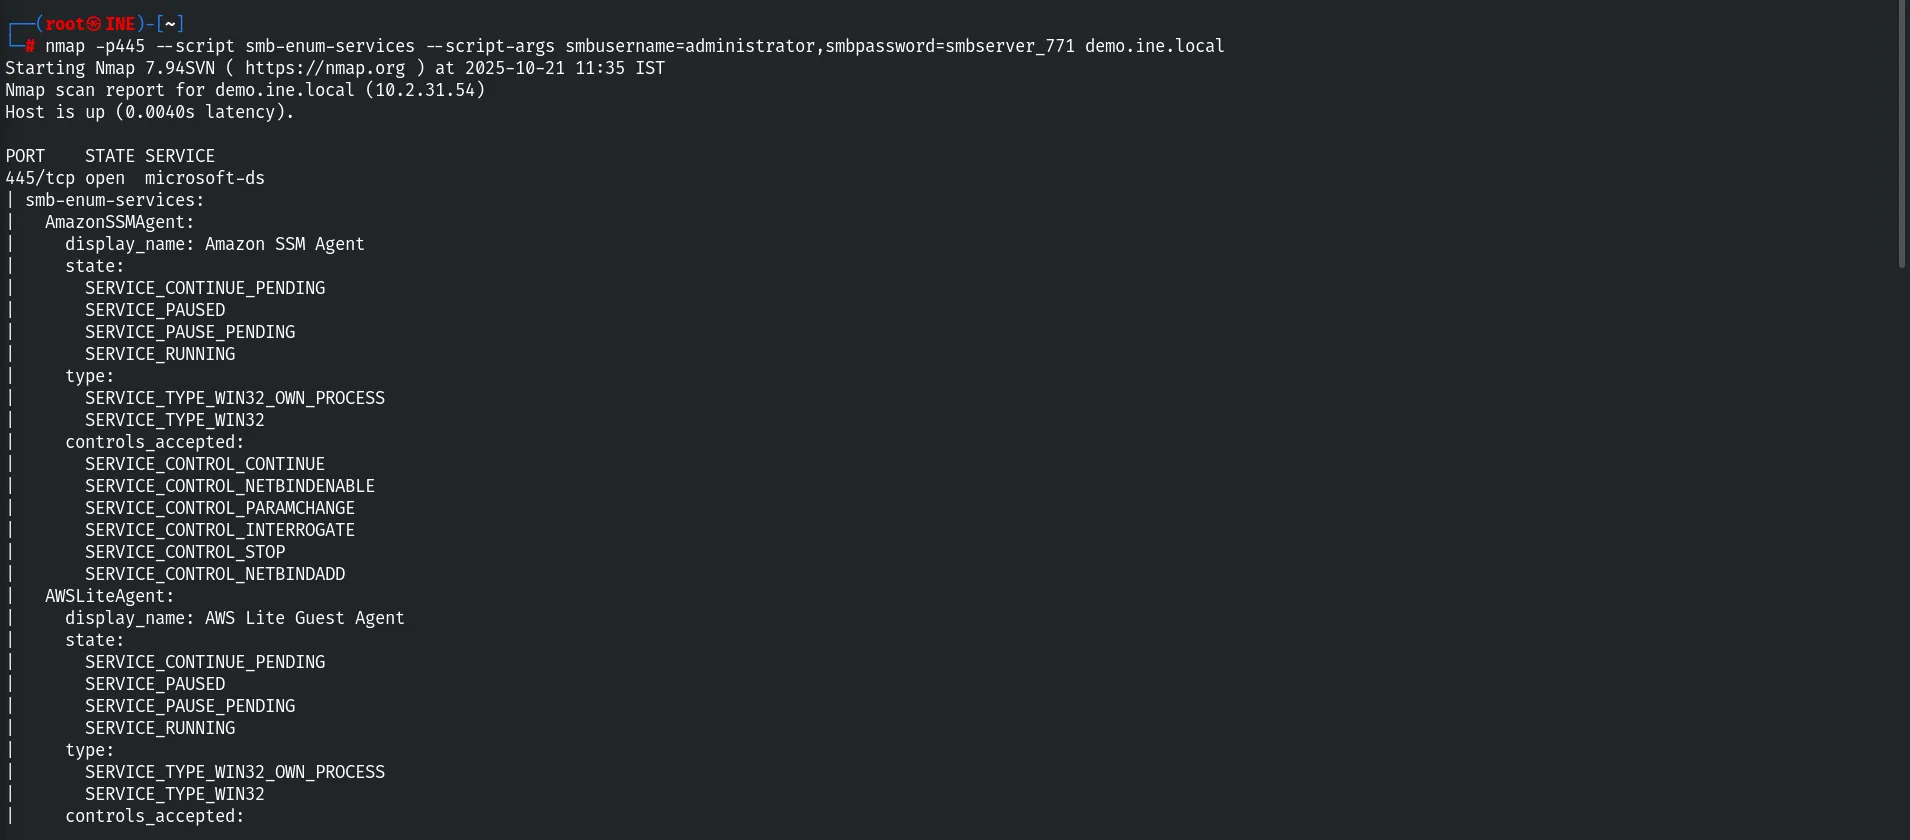
nmap -p445 --script smb-enum-services --script-args smbusername=administrator,smbpassword=smbserver_771 demo.ine.localRunning services are enumerated (Amazon SSM Agent, AWS Lite Guest Agent…).
9. Listing Share Contents
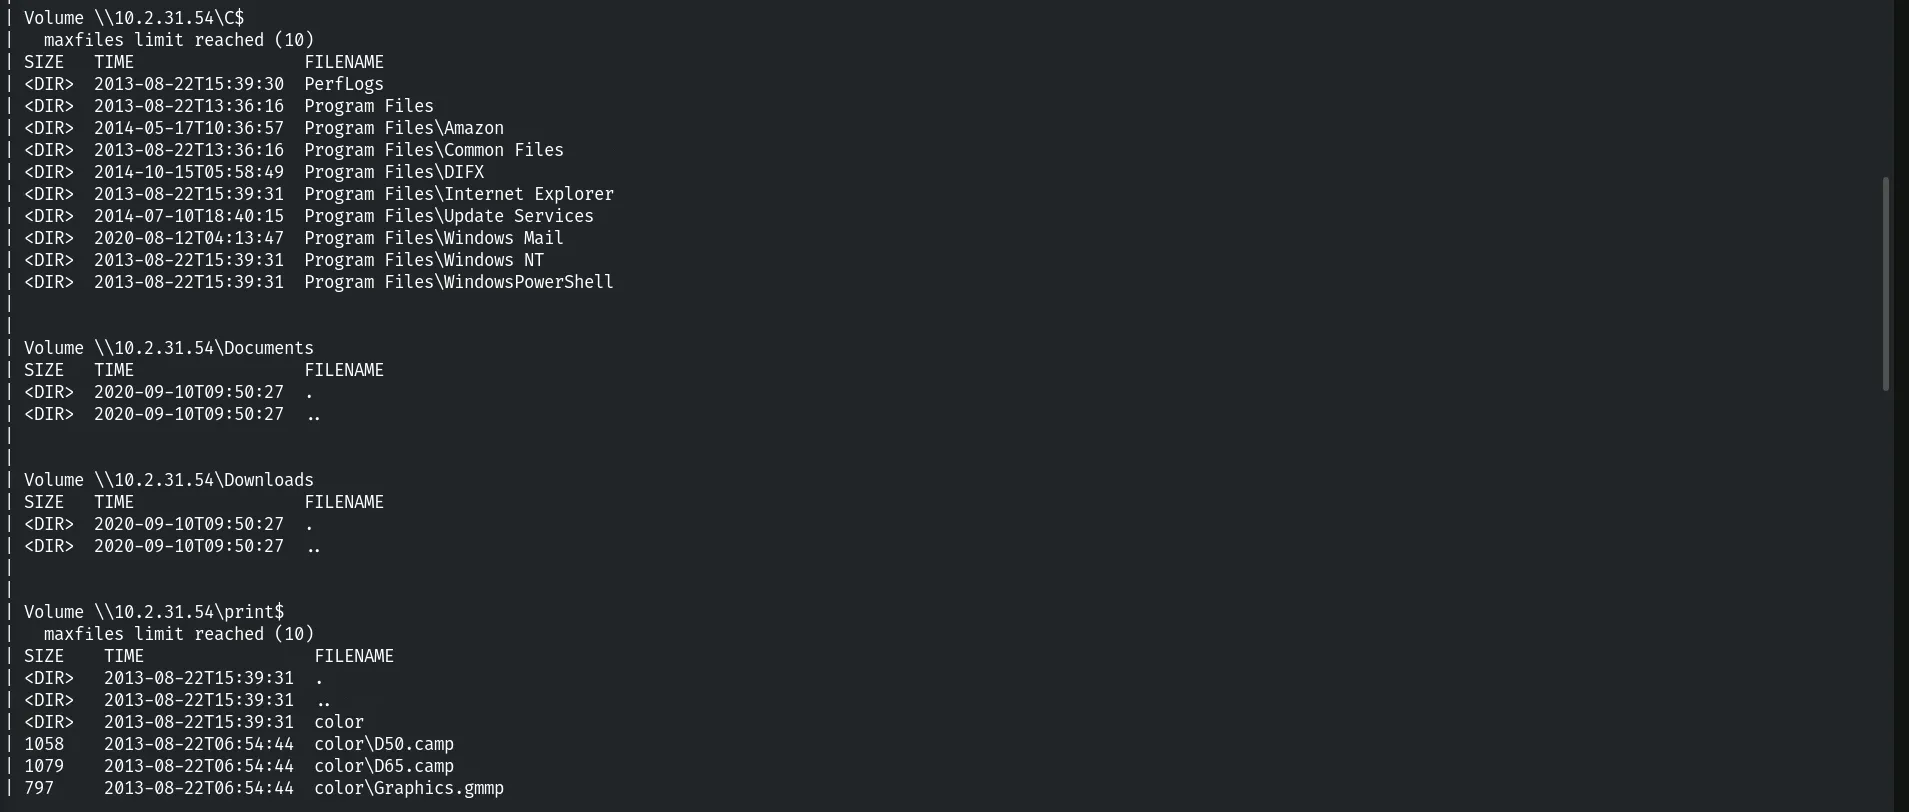
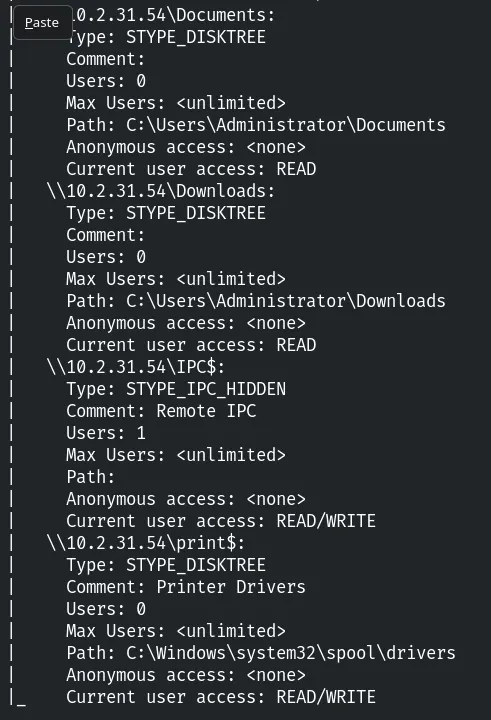
Finally we combine share enumeration with smb-ls to list the files inside each share.
nmap -p445 --script smb-enum-shares,smb-ls --script-args smbusername=administrator,smbpassword=smbserver_771 demo.ine.local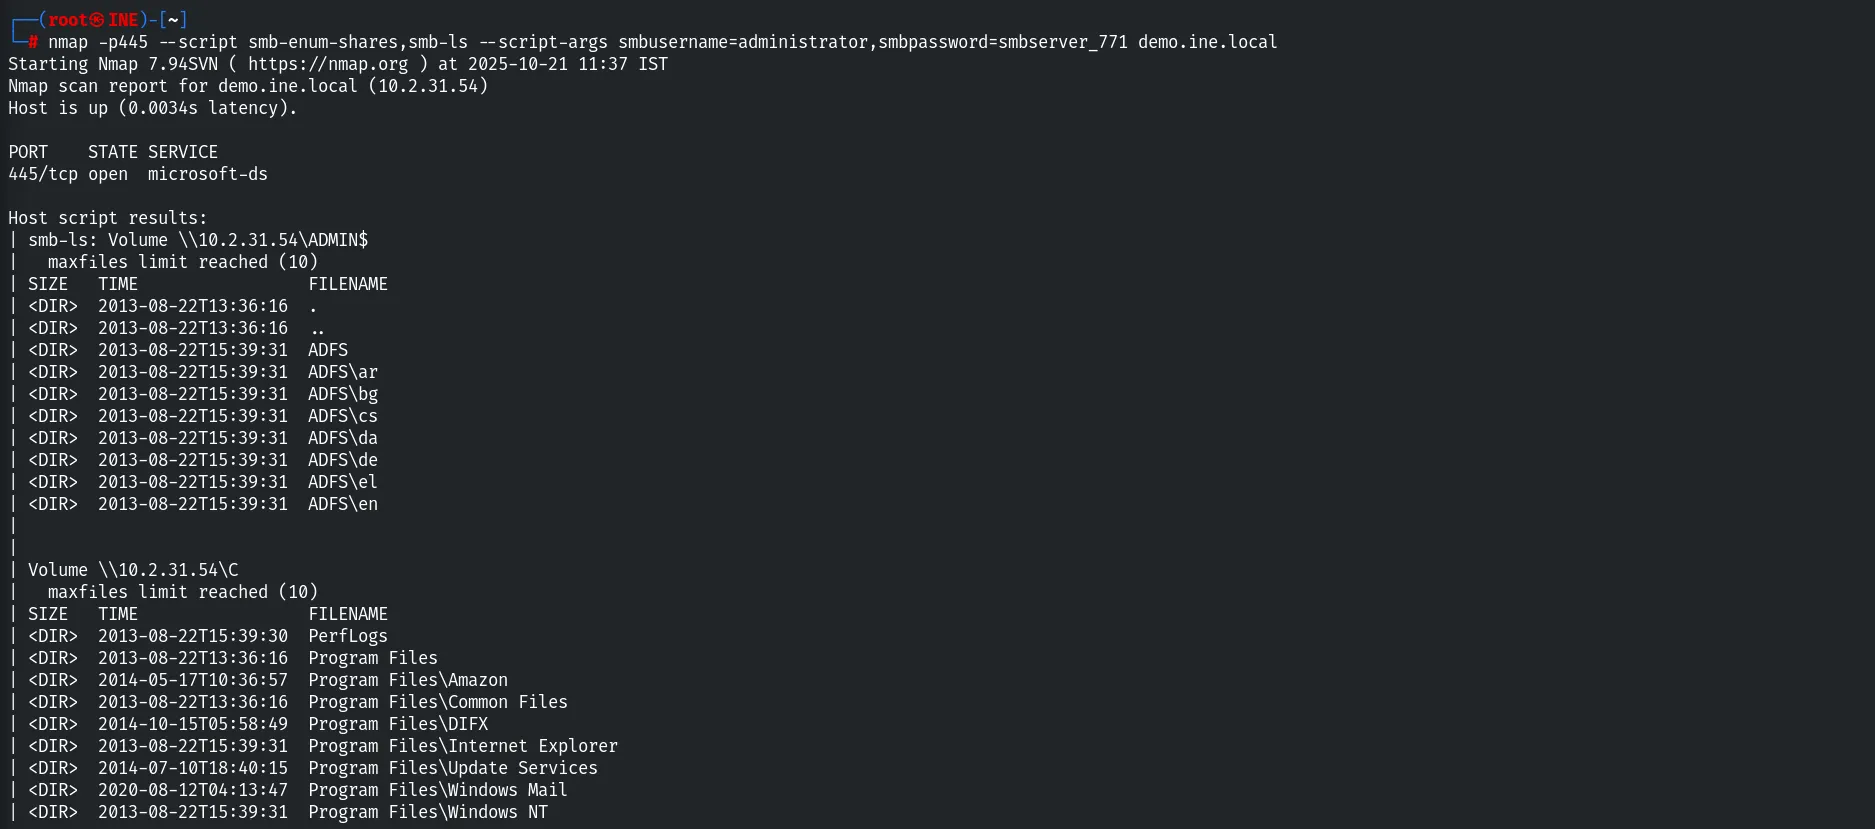
10. Remediation Recommendations
- Disable SMBv1: the legacy NT LM 0.12 dialect is dangerous and should be turned off, leaving only SMB 2/3.
- Enforce SMB signing: enable message signing to prevent SMB relay attacks.
- Enforce strong credentials and account lockout: the
administratoraccount used a weak password and account lockout is disabled. - Restrict share and administrative access: apply least-privilege permissions and
limit who can reach
ADMIN$/C$over the network. - Limit anonymous/guest enumeration so recon scripts cannot map sessions, shares and users without authentication.